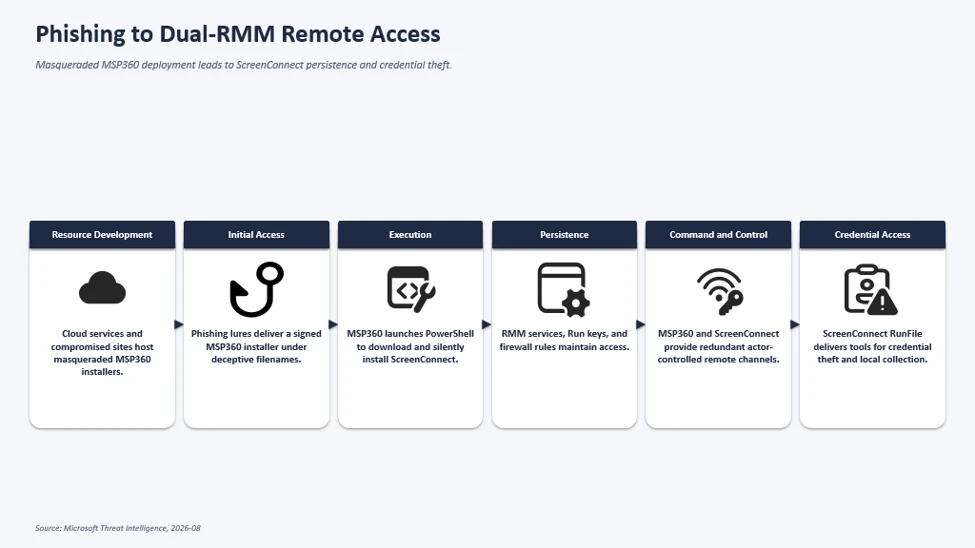
Phishing Abuses RMM Tools for Persistent Access
Microsoft observed phishing campaigns that abused MSP360 RMM to deploy ScreenConnect, creating redundant remote-access channels for follow-on activity The post Phishing Abuses RMM Tools for Persistent Access appeared first on Microsoft Security Blog .
Published by Microsoft Security BlogOpen original story
Magazine Core indexes and summarizes the source. The complete article remains with its original publisher.