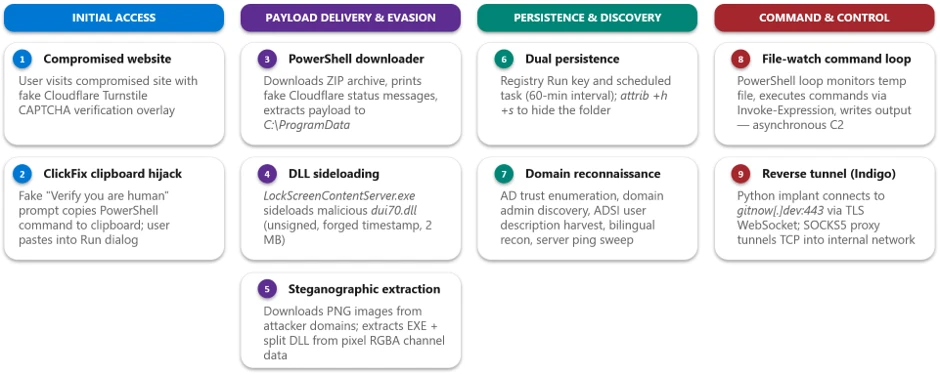
TerminalFix campaign deploys a reverse tunnel through multistage intrusion
Microsoft Threat Intelligence provides analysis of a ClickFix campaign that uses fake CAPTCHA prompts, DLL sideloading, and a reverse tunnel, with detections and hunting guidance. The post TerminalFix campaign deploys a reverse tunnel through multistage intrusion appeared first on Microsoft Security Blog .
Published by Microsoft Threat IntelligenceOpen original story
Magazine Core indexes and summarizes the source. The complete article remains with its original publisher.